
Cybersecurity
A Clear View of Your Exposure and a Plan to Reduce It
We establish what your organisation can least afford to lose, rank the risks against it and close the gaps that matter, so that security spending follows your actual exposure.
Our Point of View
Security is a decision about what an organisation can afford to lose. Once that is settled, every control and every purchase follows your actual risk.
The Situation
Most incidents begin with stolen passwords, unpatched systems or excess access, and automated attacks look for weak settings wherever they are found. Spending delivers most when it addresses those causes directly, with alerts that get read and a plan your team has already tested, ready for the moment when customers, regulators and the board all want answers together.
Our Approach
We begin by ranking which data, systems and processes would cause most harm if lost, leaked or stopped, and that ranking governs the rest of the work. Access and existing tools are tightened first, and a new product is recommended only when a specific risk justifies it. Your team then rehearses a realistic scenario, so that decisions under pressure have already been practised.
What We Deliver
From Ranked Risk to Rehearsed Response
How We Engage
A Ranked, Costed Plan in Four Weeks
Four weeks produce a risk assessment ranked by business impact and a costed plan to close the gaps. For security work, week one establishes which data, systems and processes matter most, and that ranking directs each later stage.
What Matters Most
We establish which data, systems and processes matter most to the business. That ranking directs each later stage.
Expected Outcomes
What Leadership Should Expect to See
Risk Stated in Business Terms
Exposure is ranked by business impact, so investment decisions rest on what the organisation stands to lose and customer security questionnaires can be answered with confidence.
Access That Can Be Accounted For
Single sign-on, strong login and regular reviews establish who can reach which systems, including any access still held by former staff.
A Response That Has Been Rehearsed
Your team has worked through a realistic scenario, so it is already clear who decides, who speaks and what happens first when an incident occurs.
Industries
Where This Work Applies
Customer records and access to financial systems carry direct regulatory and customer consequences, so identity controls and rehearsed escalation receive particular attention.
Patient records must remain both protected and available, so data protection and incident planning are built around the services that cannot stop.
Citizen records and public services attract scrutiny when they fail, so access reviews, data protection and clear communication during an incident carry particular weight.
Insights
Perspectives on Security Risk
Perspective · 5-minute read
Plan and Fund Security Support for a Connected Device Before You Sell It
ExpandA connected device keeps meeting new vulnerabilities after it is installed. We turn that into a ranked, costed plan, so security support is funded for as long as the device is in service.
Guide · 5-minute read
Prepare Your Systems for India's Data Protection Law: Deletion, Retention and Logs First
ExpandDiscussion of India's data protection law tends to start with consent notices. For a system owner, the harder work lies in deletion, retention and logging, and it needs lead time.
Perspective · 4-minute read
Be Able to Show Within Hours That the Plant Is Safe to Keep Running
ExpandJoining plant and office networks is now routine. We rank what matters most, record every connection and rehearse the morning of an incident, so the decision to keep running rests on evidence.
Perspective · 4-minute read
Decide in Advance Which Instant Payments Deserve a Second Look
ExpandWhen the customer authorises the payment, every sign-in check passes. We help you choose which payments deserve a second look, and test those rules on your own cases.
Perspective · 4-minute read
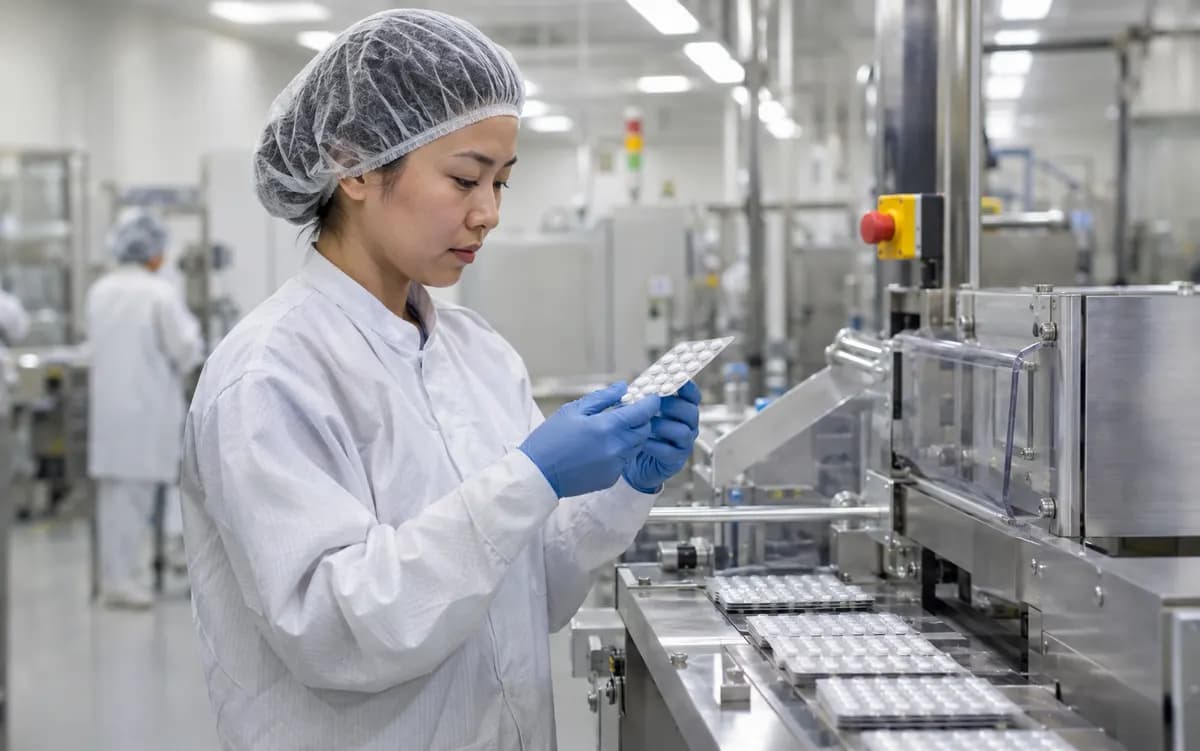
Build Named Sign-in Into the Software, So Every GMP Record Shows Who Made It
ExpandA shared login means a GMP record cannot say who made it. We treat it as a design question, and build named sign-in into the first version so the easy way to work is the attributable one.
Perspective · 4-minute read
Keep Treating Patients Through a Ransomware Outage: A Plan That Clinical Leaders Own and Rehearse
ExpandA restoration plan answers IT's question. Hospitals also need a rehearsed answer to how care continues without systems for weeks, owned by clinical leadership and covering suppliers.
Guide · 4-minute read
Data Residency Starts With Tracing Every Copy, and We Set Up Controls From the First Day
ExpandChoosing an Indian region is often treated as the answer. The rules depend on the kind of data and who holds it, and they follow every copy, so we begin by finding each one.
Perspective · 4-minute read
Security as a Business Decision: What You Can Afford to Lose, for How Long, and Who Accepts It
ExpandEvery organisation accepts some security risk, usually by default. We help you name what you can afford to lose and for how long, so spending follows your actual risk.
Frequently Asked
Questions From Prospective Clients
We Are Not a Large Organisation. Are We Really a Target?
Do We Need to Buy More Security Tools?
Will This Work Help Us Answer Customer Security Questionnaires?
How Do You Establish Whether Former Staff Still Have Access to Our Systems?
Does the Data Protection Work Follow India's Data Protection Law?
How Is Our Incident Response Plan Rehearsed?
Explore Further
Related Services
Business Consulting
Clear direction on what to change first, and a plan with named owners that your people are able to carry out.
Applications
A considered view of the application portfolio, modernised in stages, connected properly and kept running well.
AI and Automation
Applied AI for document processing, knowledge and workflow, measured on your own records before it reaches production.
Next Step
Book an Appointment
Arrange a complimentary 30-minute conversation, with no obligation. You will leave with a candid view on whether the initiative is worth building and, if it is, a scope and a date, with the cost worked out together on the call. Alternatively, send an enquiry and we will respond.